Ukraine’s drone strikes on Russian data centers triggered a remarkable drop in automated internet traffic, followed by claims that Russian propaganda networks had suddenly gone quiet. While the infrastructure damage certainly occurred, the framing of the whole event is still up to interpretation.
Over the past week, something rather unusual happened on the internet. Following a series of Ukrainian drone strikes against Russian data centers operated by Yandex, charts began circulating on social media showing an enormous decline in automated traffic originating from the company’s networks. Almost immediately, people started celebrating what appeared to be the sudden disappearance of Russian propaganda bots from Western social media.
The implications were tantalizing. Had Ukraine managed to accomplish with a handful of drones what years of content moderation, cybersecurity research, and government investigations had failed to achieve? Had the Russian disinformation machine, responsible for years of election interference, conspiracy theories, and coordinated political manipulation, finally been knocked offline?
It made for a hell of a story, particularly for anyone who’s spent time watching suspiciously coordinated political accounts flood comment sections with identical talking points. Unfortunately, the available evidence tells a considerably more complicated story, and one that says almost as much about our collective understanding of internet infrastructure as it does about Russian propaganda.
So, what actually happened to Yandex? Between October 7 and October 11, Ukrainian drones struck three Russian data centers operated by Yandex, the technology company often described as Russia’s equivalent of Google. The strikes caused substantial disruptions to the company’s infrastructure, taking portions of its services offline and affecting businesses that depend on its computing and networking capabilities.
Yandex operates far more than a search engine. Its services include cloud hosting, online payments, transportation platforms, food delivery, and the various pieces of infrastructure that support Russia’s domestic internet economy. When a company of that size experiences a major infrastructure failure, the consequences can extend well beyond its own websites.
The attacks reportedly disrupted Russian banking services, retailers, and other online platforms. Some Yandex services became unavailable, and the extent of the physical damage raised questions about how quickly the affected infrastructure could be restored. These were significant strikes against Russia’s digital economy, regardless of whether a single propaganda account stopped posting.
This was confirmed with the traffic data. Cloudflare Radar, which provides visibility into internet traffic patterns across its global infrastructure, recorded a dramatic decline in automated requests originating from Yandex’s network. According to research published by Graphika on October 13, the observed traffic fell to approximately 0.4% of its recent peak by October 11.
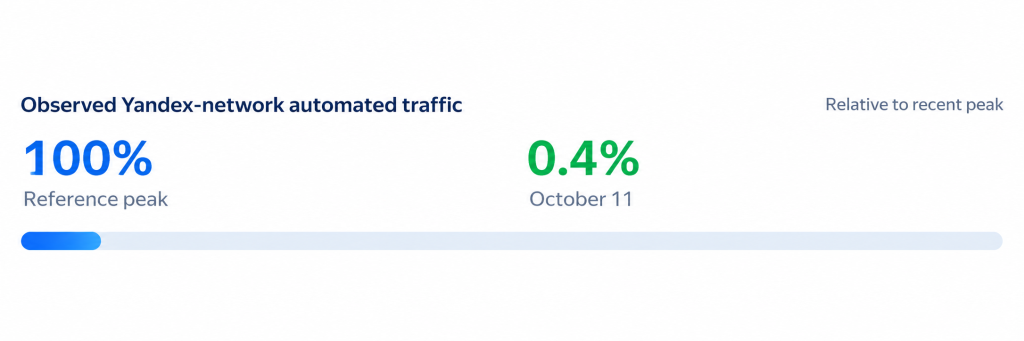
That’s an extraordinary reduction in activity, and the timing closely aligned with the drone strikes. Independent cybersecurity researchers at WebDecoy subsequently reported a similar pattern in their own monitoring, observing that requests from Yandex’s search crawler had fallen 94% on October 8 before disappearing from their sensors on October 10. The evidence that Yandex’s automated systems were severely disrupted is compelling. But the assumption that these systems were responsible for coordinating Russian political influence campaigns is where the story begins to unravel.
It’s important to note, not all bots are propaganda bots. The word “bot” has acquired a distinctly negative reputation, which is understandable given the sheer volume of malicious automation operating across the internet. Spam campaigns, credential-stuffing attacks, fake engagement, coordinated harassment, and social media manipulation all make extensive use of automated systems.
But the overwhelming majority of people encounter legitimate bots every day without realizing it. Search engines use automated crawlers to discover and index websites, security companies use automated systems to inspect threats, and businesses use bots for monitoring, customer service, and routine administrative tasks.
Yandex operates its own web crawler, YandexBot, which performs essentially the same basic function as Google’s Googlebot. It visits websites, discovers new pages, and collects information that can be incorporated into search results. This activity generates large volumes of automated traffic, particularly from the networks hosting the search engine’s infrastructure.
When Yandex’s data centers went offline, its crawlers predictably stopped making many of those requests. The resulting traffic graphs looked dramatic because the disruption itself was dramatic.
But measuring requests from a search engine’s network tells us very little about whether coordinated political accounts on X, Reddit, Facebook, or other social platforms have stopped publishing content. Those accounts can be operated from completely different infrastructure, using cloud hosting providers, proxy services, compromised devices, or ordinary residential internet connections.
A Russian influence operation doesn’t have to run on Russian infrastructure at all. In fact, using geographically distributed infrastructure can make a coordinated campaign substantially more difficult to detect and attribute.
The mistake was treating two very different types of automation as though they were interchangeable. A search crawler going offline is a measurable infrastructure event. A disinformation network going offline requires evidence about the behavior of the accounts participating in that network.
Unfortunately, the data doesn’t quite confirm the extraordinary claims being made. As the claims spread, researchers who actually monitor online influence operations began investigating whether the alleged disappearance of propaganda accounts could be substantiated.
New data emerging from CloudFlare after the event shows that instead of going dark, bots actually pivoted. Overall bot traffic was down, but unfortunately there’s no evidence the malicious bot traffic everyone is concerned with actually subsided very much. This possibly suggests the bad actors maintaining these operations have contingency plans for their malfeasance.
Meanwhile, mentions of MAGA on X actually increased by 25% during the first eight hours following one of the strikes, compared with the equivalent periods on the previous four Sundays. In other words, bot manipulation appeared to not only survive the disruption but actually increased in response to it.
Other researchers reached similar conclusions. Amil Khan, CEO of the disinformation-monitoring company Valent, told The Guardian that his organization’s monitoring of approximately 40 influence networks had identified no discernible change in posting patterns.
That doesn’t conclusively prove the strikes had no effect on Russian information operations. A particular service or smaller network could have been disrupted without producing an obvious change across the larger datasets. Access to social media data is also limited, making comprehensive measurements difficult.
It does, however, leave the central viral claim without the evidence necessary to support it. This is how one story became a viral moment, one of the more interesting aspects of this incident is how quickly a legitimate technical observation evolved into an entirely different narrative.
First, Ukrainian drones damaged Russian digital infrastructure. Next, automated network traffic declined dramatically, an outcome consistent with the loss of major computing facilities. Then screenshots of those measurements circulated with claims that pro-Russian political activity had collapsed across Western social media.
By the time the story reached broader audiences, the distinction between Yandex’s search crawlers and social media propaganda operations had largely disappeared.
Ukrainian President Volodymyr Zelenskyy contributed to the enthusiasm when he suggested that the strikes had made social media feel noticeably less hostile, with fewer provocations and divisive exchanges. His observations resonated with people who had already noticed what they believed was an improvement in the quality of online conversations.
The problem is that personal impressions are poor substitutes for systematic measurements. Social media engagement changes throughout the day, political discussions fluctuate in response to news events, and accounts can become more or less active for reasons entirely unrelated to physical infrastructure.
The episode also illustrates how easily statistics can be stripped of their original context. Some of the viral charts purported to show enormous reductions in activity associated with European political parties despite lacking clear sourcing, methodology, or even plausible timelines. In one example examined by Graphika, a chart included data points dated after the post that originally shared it.
That should have raised a few eyebrows. Instead, the charts accumulated millions of views, propelled in part by the understandable desire to believe that an enormous source of online manipulation had abruptly disappeared. There’s a certain irony in using misleading interpretations of internet traffic to celebrate the supposed defeat of disinformation.
None of this diminishes the importance of what Ukraine actually accomplished, the strikes were still a significant technological blow to Russia. Data centers are enormously valuable infrastructure. They house the computing systems, storage equipment, networking hardware, and supporting services on which businesses and government operations increasingly depend. They also require substantial electrical capacity, cooling systems, physical security, and reliable connectivity.
Replacing damaged servers is one problem. Restoring an entire facility, its electrical infrastructure, network interconnections, and operational capacity is another matter entirely. Even where redundant systems exist, losing multiple facilities within a short period can overwhelm disaster recovery arrangements and expose dependencies that weren’t obvious when everything was functioning normally.
There’s also a broader strategic dimension. Ukraine has demonstrated an ability to reach infrastructure deep inside Russian territory, targeting assets that contribute to the country’s economic stability and technological capabilities. Digital services can be just as important to modern economies as traditional industrial infrastructure, and prolonged disruptions can impose costs well beyond the physical damage inflicted.
For years, much of the public discussion about cyber warfare has focused on hackers penetrating networks and disabling systems through software. The Yandex attacks offer a rather different demonstration of the relationship between physical infrastructure and digital availability.
All the encryption, network segmentation, endpoint protection, and intrusion detection in the world won’t keep your applications running when the facility hosting them has been physically destroyed. Geographic redundancy and well-tested recovery arrangements become particularly important when infrastructure itself is an increasingly attractive target.
And it’s worth remembering that Russian attacks have also damaged Ukrainian infrastructure, including systems supporting civilian communications and other essential services. The vulnerability isn’t unique to either side.
These events are part of a larger evolution in warfare, where data centers, telecommunications systems, cloud services, and satellite networks have become strategically important assets rather than merely supporting technologies.
Meanwhile while this Yandex story was circulating, a separate development raised equally important questions about Ukraine’s dependence on foreign-controlled technology. On October 14, Ukrainian officials reported that restrictions affecting SpaceX’s Starlink satellite communications services had disrupted military operations. According to Reuters, the changes particularly affected high-speed drones using satellite connectivity for navigation, communications, and battlefield coordination.
Serhiy Beskrestnov, an adviser to Zelenskyy, reported that the restrictions affected military-grade systems operating above approximately 160 kilometers per hour, or 100 miles per hour. Ukrainian military personnel also described shorter interruptions at lower speeds, with connection losses lasting 10 to 20 seconds during flight.
These aren’t insignificant disruptions. For a drone traveling at high speed, a brief loss of connectivity can interfere with guidance, prevent course corrections, or force operators to abandon a mission entirely. Ukrainian units reported that several operations had already been canceled as a consequence.
The situation became particularly contentious because the restrictions appeared amid growing tensions between Washington and Kyiv over Ukrainian strikes against Russian energy infrastructure.
Elon Musk subsequently argued that Starshield, the military-focused satellite service associated with SpaceX, is controlled by the United States government and that restrictions on its operation are determined by American military authorities. The White House, however, denied ordering the restrictions, reportedly attributing the situation to a technical issue.
As of October 15, there’s an important update. Axios reports that both Starlink and Starshield services have been restored to full capacity, citing a Ukrainian official. The reported restoration followed more than a day of disruption, although questions remain about who authorized the restrictions, why they were implemented, and whether they could recur.
It’s important to emphasize that information about this incident is still developing. The technical restrictions and their immediate operational consequences have been reported by multiple outlets, but the competing explanations surrounding their origin have not been independently resolved. Claims that the restrictions were deliberately imposed as political leverage against Ukraine should be treated as allegations rather than established facts.
There’s also an important distinction between commercial Starlink service and the military-oriented Starshield system. Although the two share underlying technology, they operate under different contractual and operational arrangements. Conflating them risks introducing the same kind of confusion that surrounded the Yandex bot-traffic claims.
Nevertheless, the broader implications are difficult to ignore.
Ukraine has become heavily dependent on satellite communications to sustain military operations in an environment where terrestrial networks can be damaged, disrupted, or subjected to electronic warfare. Starlink has played a crucial role in maintaining those communications since Russia’s full-scale invasion began in 2022.
When critical capabilities depend on infrastructure controlled by an external provider or government, decisions made thousands of miles from the battlefield can have immediate consequences for soldiers operating on the front line.
Europe has discussed alternative satellite capabilities, including Eutelsat’s OneWeb network and longer-term European satellite projects, but replacing Starlink at scale is neither a quick nor straightforward proposition. According to Reuters, technical limitations, incompatible equipment, and deployment requirements present substantial obstacles to an immediate transition.
The comparison with Yandex is particularly revealing. In Russia’s case, physical attacks disrupted infrastructure supporting commercial services. In Ukraine’s case, reported restrictions on satellite communications disrupted services supporting military operations, without requiring an attack on the satellites or their ground infrastructure.
Different mechanisms, certainly, but both demonstrate how much power rests with whoever controls the underlying technology.
There’s a temptation to frame the Yandex strikes as a decisive victory against Russia’s online propaganda apparatus. Doing so offers a particularly satisfying explanation for a measurable decline in bot traffic, especially given the documented history of Russian influence operations targeting Western democracies.
Researchers examining the relevant political communities have found little to support that conclusion, and the most widely circulated statistics weren’t measuring propaganda activity in the first place. It should be noted whether it’s worth changing that going forward, particularly with the response this story has generated. The community appears to be hungry for a reduction in bot traffic and any inkling of relief led to a ripple effect across the internet which was undeniable.
The Starlink controversy raises a related but somewhat different concern. Modern warfare is increasingly dependent on technologies controlled by private companies, third-party infrastructure providers, and governments whose priorities don’t always align with those of the people relying on their services.
For organizations outside the military, the lesson is familiar. Understanding who controls your infrastructure, what dependencies exist, and how you would operate if a critical service became unavailable is an essential part of managing technological risk.
For Ukraine, those questions have consequences measured in lost military capabilities and potentially human lives. For Russia, the Yandex strikes demonstrate that even a substantial domestic technology ecosystem remains vulnerable to physical disruption. And for everyone watching these events unfold online, the propaganda-bot controversy offers a reminder that interpreting technical evidence requires a little more effort than reading the headline attached to a viral chart.
While this story deviates from our core offering as a technology provider, it is a stark reminder that everyone is vulnerable to disruptions in our shared technological space. Protecting your network protects your business from unnecessary disruptions. At Valley Techlogic, supporting your existing technology and protecting your business from threat vectors is a core component of all of all service plans because we know preventing threats from happening in the first place is preferable to responding to a threat that has already taken place. Learn more today with a consultation.
Editorial note: This article reflects reporting available on October 15, 2026. Details regarding the Starlink and Starshield restrictions, their authorization, and their operational consequences remain subject to further verification.
- Email scams have grown more sophisticated and realistic, here are 5 ways you can still tell
- Meta announced Muse and OpenAI announced Dots, are cutesy avatars the way to mass market appeal with real world application or a cheap gimmick?
- 6 Reasons to restrict admin access to company devices
- Is the AI threat overblown? Why OpenAI, Anthropic and more are cautioning we need to “slow down” on AI innovation and focus on safety
- ChatGPT’s Astra (GPT-6) has been released, is it worth the hype?
This article was powered by Valley Techlogic, leading provider of trouble free IT services for businesses in California including Merced, Fresno, Stockton & More. You can find more information at https://www.valleytechlogic.com/ or on Facebook at https://www.facebook.com/valleytechlogic/ . Follow us on X at https://x.com/valleytechlogic